CI/CD DAST Without Slowing Software Delivery
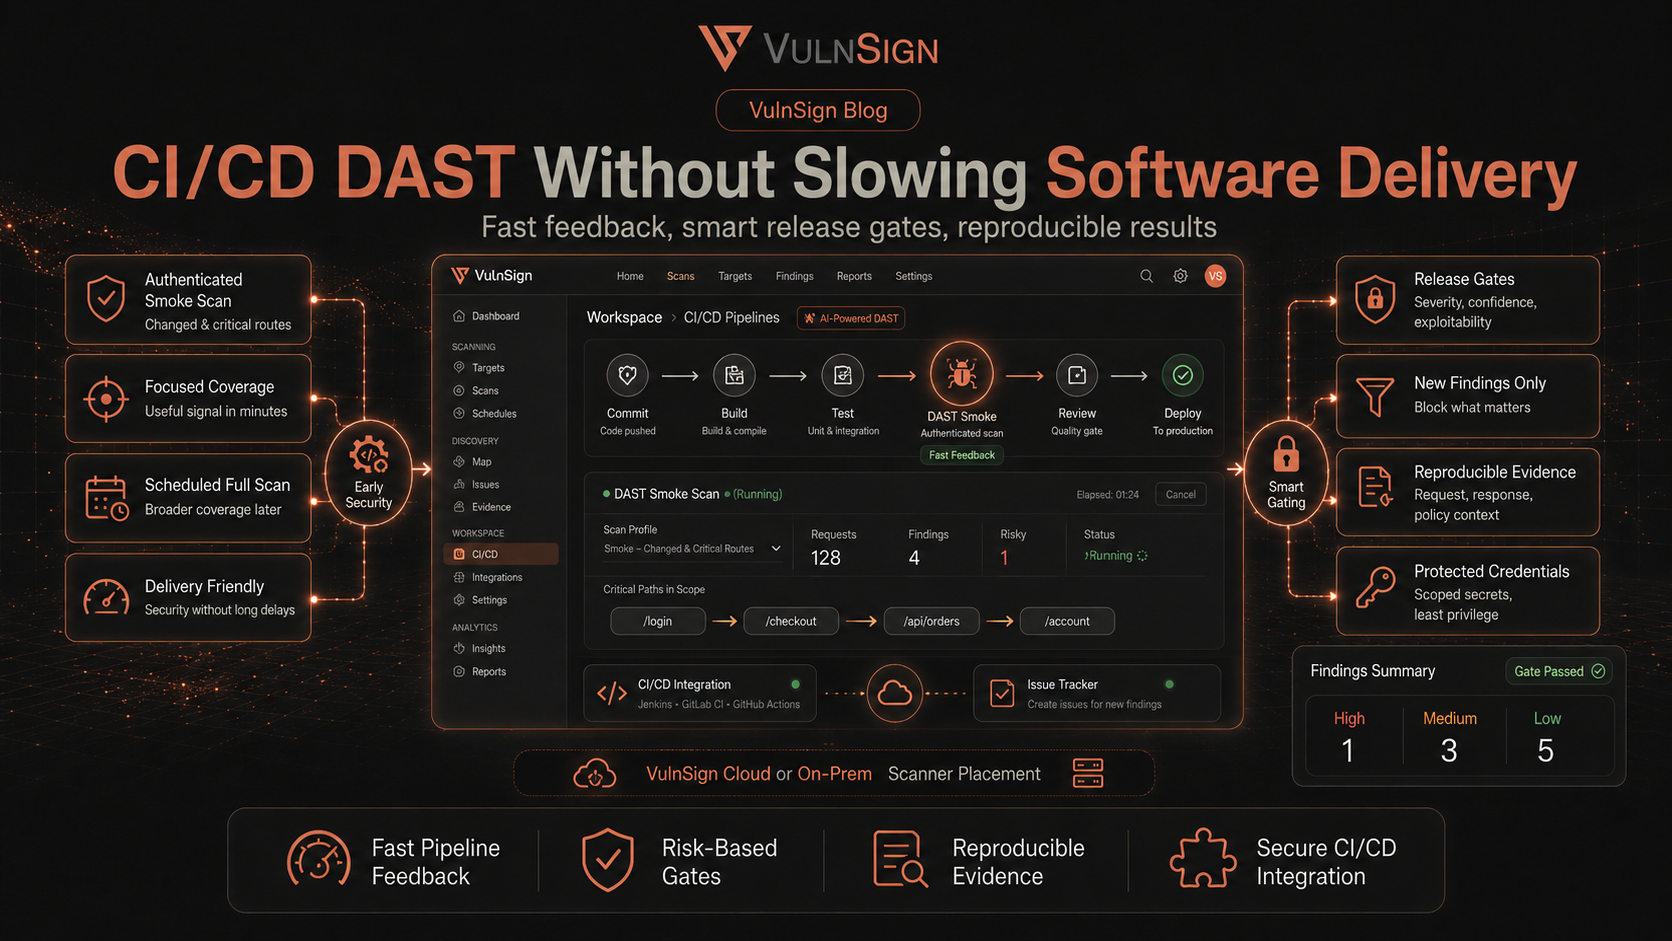
Start with feedback, not a giant scan
A delivery pipeline needs a focused security signal within a useful time window. Begin with a small authenticated smoke policy for changed or critical routes, then run broader coverage on a schedule or in a dedicated environment.
Separate discovery from release gates
Not every observation should block a release. Define gates using severity, confidence, exploitability, and whether a finding is new. Route lower-priority findings into the normal remediation workflow rather than making developers ignore an all-or-nothing gate.
Make results reproducible
A useful pipeline finding includes the affected target, request and response evidence, policy context, and a stable path to retest. VulnSign integrations connect scan outcomes with issue trackers and CI/CD workflows while retaining the technical evidence for AppSec review.
Protect pipeline credentials
Use least-privilege test identities, separate environments, scoped secrets, and clear data-retention rules. For private targets, select VulnSign Cloud connectivity or on-premise scanner placement based on network and compliance requirements.
Related Articles
Explore more insights, strategies, and perspectives related to this topic.
Questions before you scan?
Learn how VulnSign fits into your environment, security workflow, and team.
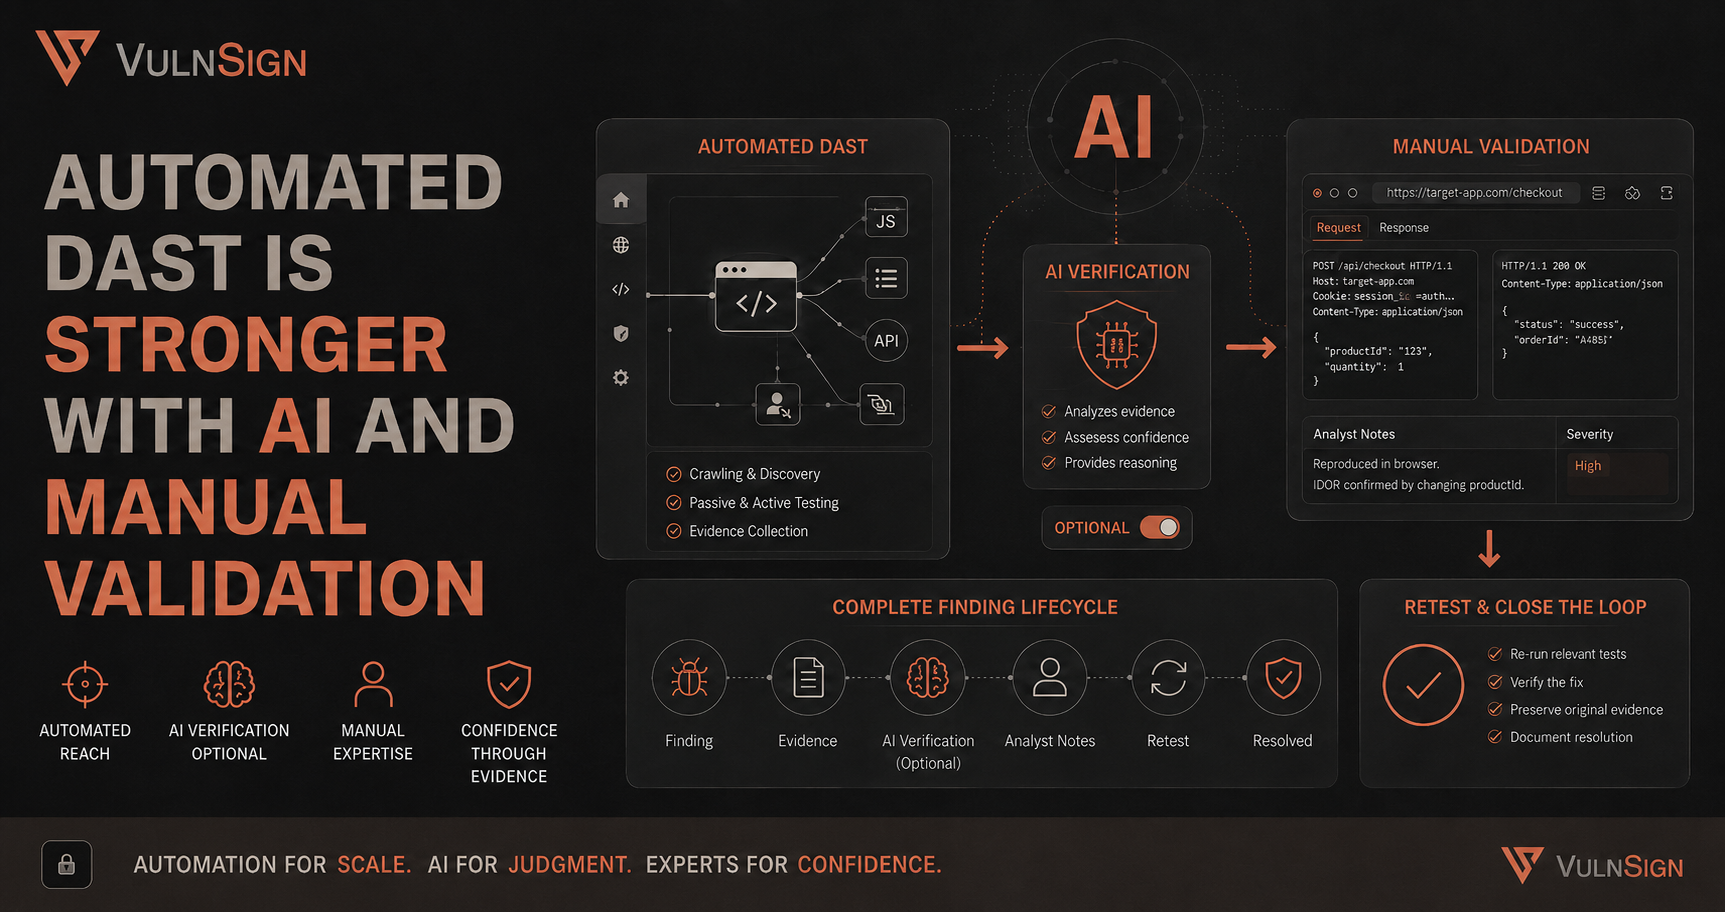
Put automated and manual testing in one workflow.
See how VulnSign helps your team discover more attack surface, validate risk, and move findings to remediation—without sending security data to a cloud control plane.