Where AI-native DASTmeets manual pentestingin the cloud or on-prem.
From Vuln to Sign—detect, validate, fix, and verify vulnerabilities with AI.
EveryVulnerability Signal.One Platform.
Connect security testing to your delivery workflow.
Connect CI/CD pipelines, issue trackers, scanner agents, and API-driven automation. Keep security findings moving from discovery to the teams that fix them.
See the application through an attacker’s eyes
Bring discovery, scanner activity, HTTP traffic, findings, and remediation status into one live workspace. Move from automated evidence to hands-on validation without losing context.
Everything your team needs to act on risk
Monitor scans, attack surface, findings, and remediation from a single operational view.
Active scans
4
2 authenticated · 2 scheduled
Open findings
126
8 critical · 24 high
Verified findings
72%
Validated by scanner or analyst
Requests tested
125K
Across web and API targets
Production API scan
Active testing completed
Authentication bypass
Assigned to AppSec
Customer portal
Crawler discovered 48 routes
Stored XSS
Fix submitted for retest
See risk clearly. Act from one workspace.
Follow attack surface, scan coverage, findings, and remediation with technical evidence your team can act on.
VulnDetectValidateFixVerifySign
One continuous application security workflow
VulnSign automatically discovers your attack surface, detects vulnerabilities, validates what is real, fixes the underlying issue, verifies the remediation, and turns trusted findings into action—all in one continuous workflow.
Map the attack surface
VulnSign automatically maps routes, forms, APIs, WebSockets, technologies, ports, subdomains, and hidden exposure with real-browser crawling and attack-surface discovery.
Find vulnerabilities at scale
VulnSign automatically runs active and passive security tests across the discovered attack surface to identify vulnerabilities, misconfigurations, and suspicious application behavior.
Separate signals from real risk
VulnSign automatically reproduces findings, analyzes evidence with AI, connects attack paths, and prioritizes issues based on exploitability, context, and business impact.
Remediate the vulnerability
VulnSign automatically fixes the vulnerable code or configuration while keeping the remediation connected to the finding and its supporting evidence.
Prove the fix works
VulnSign automatically retests the endpoint and confirms that the vulnerability can no longer be reproduced.
Turn validated findings into trusted action
VulnSign automatically signs off on verified findings and preserves the complete evidence trail in the same workspace.
Built for security teams that need automation and control
VulnSign combines automated DAST with a complete manual pentest workspace. Run it offline on your operating system, manage it from the GUI, and collaborate through the browser across your local network.
Live target
app.example.com
AI that participates in the security workflow—not just the report.
Orchestrate targets in natural language, triage findings while scans run, correlate attack paths, and produce audience-ready security narratives. Use Claude or keep inference completely local with Ollama.
VulnSign AI Assistant
Local model connected
12 targets selected
Technology-aware profiles prepared
Attack chains enabled
Cross-finding correlation
Report intelligence
Executive summary on completion
Why we stand out
Compare VulnSign with Invicti and Burp Suite across automation, analyst tooling, discovery, AI-assisted workflows, remediation operations, and deployment choice.
VulnTarget benchmark snapshot
Observed results from the same target with 10 known vulnerabilities. Request totals for Invicti and Burp Suite were recorded as tens of thousands; they are shown conservatively as 10k+. Request strategy distinguishes targeted coverage from high-volume payloads sent to irrelevant resources.
 Invicti
5/10 found- Requests
- 10k+
- Scan time
- 1 hour
- Request strategy
- Untargeted SQLi attempts on robots.txt and nonexistent URLs
- Payloads
- Legacy patterns; no bypass rules
 VulnSign
10/10 found- Requests
- 500
- Scan time
- 10 min
- Request strategy
- Targeted payloads on relevant, validated inputs
- Payloads
- Modern, bypass-aware rules
 Burp Suite
3/10 found- Requests
- 10k+
- Scan time
- 2 hours
- Request strategy
- Untargeted SQLi attempts on robots.txt and broad crawl paths
- Payloads
- Legacy patterns; no bypass rules
Choose the VulnSign edition for your team
Start with Community, equip AppSec teams with Professional, or scale security operations with Enterprise.
Community
For individual security practitioners who want a capable local DAST and manual testing workspace.
Free
- Advanced manual pentesting workspace
- Active & passive scanning
- Real-browser spider crawl
- HTTP proxy & request history
- Quick port and subdomain scans
- Technology fingerprinting
- Basic HTML reporting
ProfessionalPopular
For AppSec teams that need 64 features across advanced testing, automation, AI, and reporting.
- Everything in Community
- Mobile penetration testing
- 25 targets, 10 users & 3 concurrent scans
- Custom scan profiles, policies & payloads
- Scheduled scans, issue retest & scan diff
- Replacer, Intruder, breakpoints & WebSocket
- Full port, subdomain & Android testing
- AI assistant, bulk triage & issue chat
- Full technical & executive reporting
- CI/CD & issue tracker integrations
- Roles, approvals, health info & system logs
Enterprise
For organizations that need the complete 76-feature platform, governance, and scale.
Custom
- Everything in Professional, without limits
- All 76 platform features
- AI scan planner & attack chains
- Distributed scanner agents & unlimited scale
- Multi-persona authentication
- Custom roles, trends & backup
- Bypass attack strength
- Premium Support & Custom SLA
Security teams rely on VulnSign
From CI/CD security gates to detailed vulnerability validation, teams use VulnSign to find and resolve risk before applications reach production.
“
VulnSign has become part of our release routine. The team gets a clear view of what needs attention, and developers can move straight from a finding to the relevant remediation detail.
Sahibinden
Cyber Security Director
“
Getting scans into the pipeline was refreshingly straightforward. Results arrive early enough for the right team to act, without turning every release into a security meeting.
Envato
DevSecOps Lead
“
Our developers care about context, not another long list of alerts. VulnSign gives them practical evidence and a sensible place to start, which makes security conversations much more productive.
Trendyol
Head of Software Engineering
“
Before VulnSign, checking a last-minute change could slow the whole release down. Now the scan fits into the way the team already works and the feedback is available while the change is still fresh.
ÇiçekSepeti
Chief Technology Officer
“
What stands out is how easy it is to follow a finding from detection to resolution. That visibility helps us focus on real exposure and keeps follow-up work from disappearing between teams.
Migros
Cyber Security Director
“
The reports are detailed without being difficult to use. Engineers can reproduce an issue, understand its impact, and verify the fix without waiting for a separate explanation from the security team.
Vatan Computer
Chief Technology Officer
“
VulnSign enables Justlife to test every release, fully integrated into their CI/CD toolchain. Rather than deploying code with an uncertain security state, Justlife now gets alerts for detected vulnerabilities before going live.
Justlife
VP of Engineering
“
Release windows leave little room for vague results. VulnSign gives us focused findings we can assess quickly, so security checks feel like part of delivery rather than a step added at the end.
Matriks
Software Engineering Director
“
What stands out is how easy it is to follow a finding from detection to resolution. That visibility helps us focus on real exposure and keeps follow-up work from disappearing between teams.
Migros
Cyber Security Director
“
The reports are detailed without being difficult to use. Engineers can reproduce an issue, understand its impact, and verify the fix without waiting for a separate explanation from the security team.
Vatan Computer
Chief Technology Officer
“
VulnSign enables Justlife to test every release, fully integrated into their CI/CD toolchain. Rather than deploying code with an uncertain security state, Justlife now gets alerts for detected vulnerabilities before going live.
Justlife
VP of Engineering
“
Release windows leave little room for vague results. VulnSign gives us focused findings we can assess quickly, so security checks feel like part of delivery rather than a step added at the end.
Matriks
Software Engineering Director
Security research & expert insight
Explore application security research, practical DAST guidance, and technical insight for modern security teams
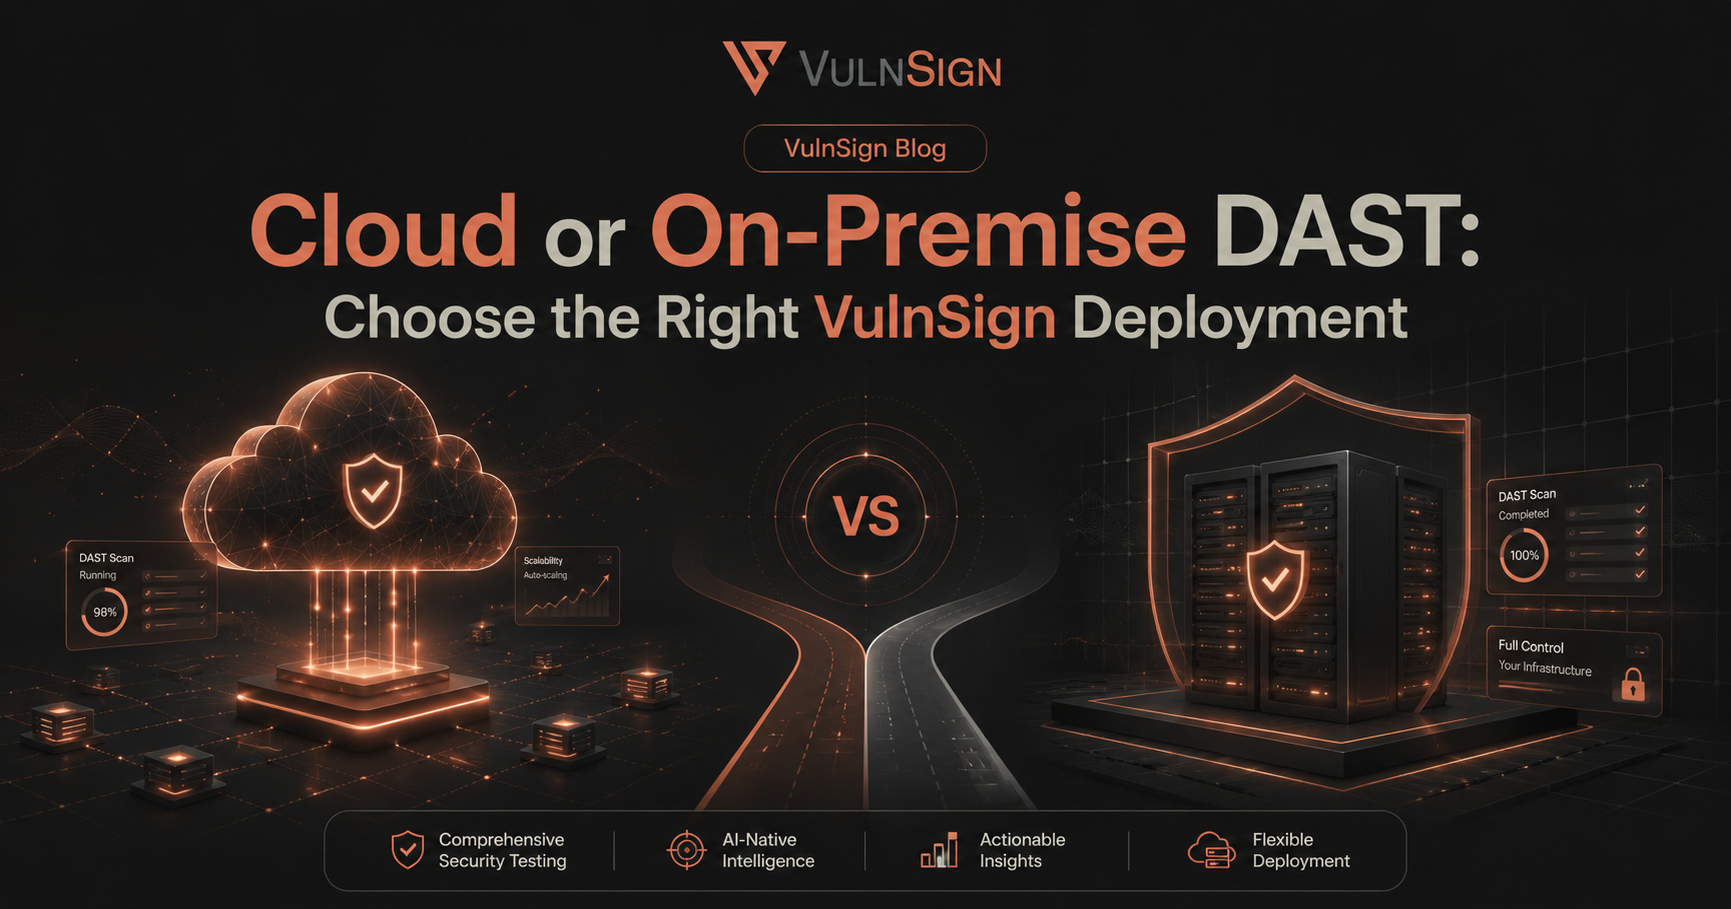
Cloud or On-Premise DAST: Choose the Right VulnSign Deployment
Compare operational control, data residency, scaling, and maintenance when deploying VulnSign Cloud or on-premise.
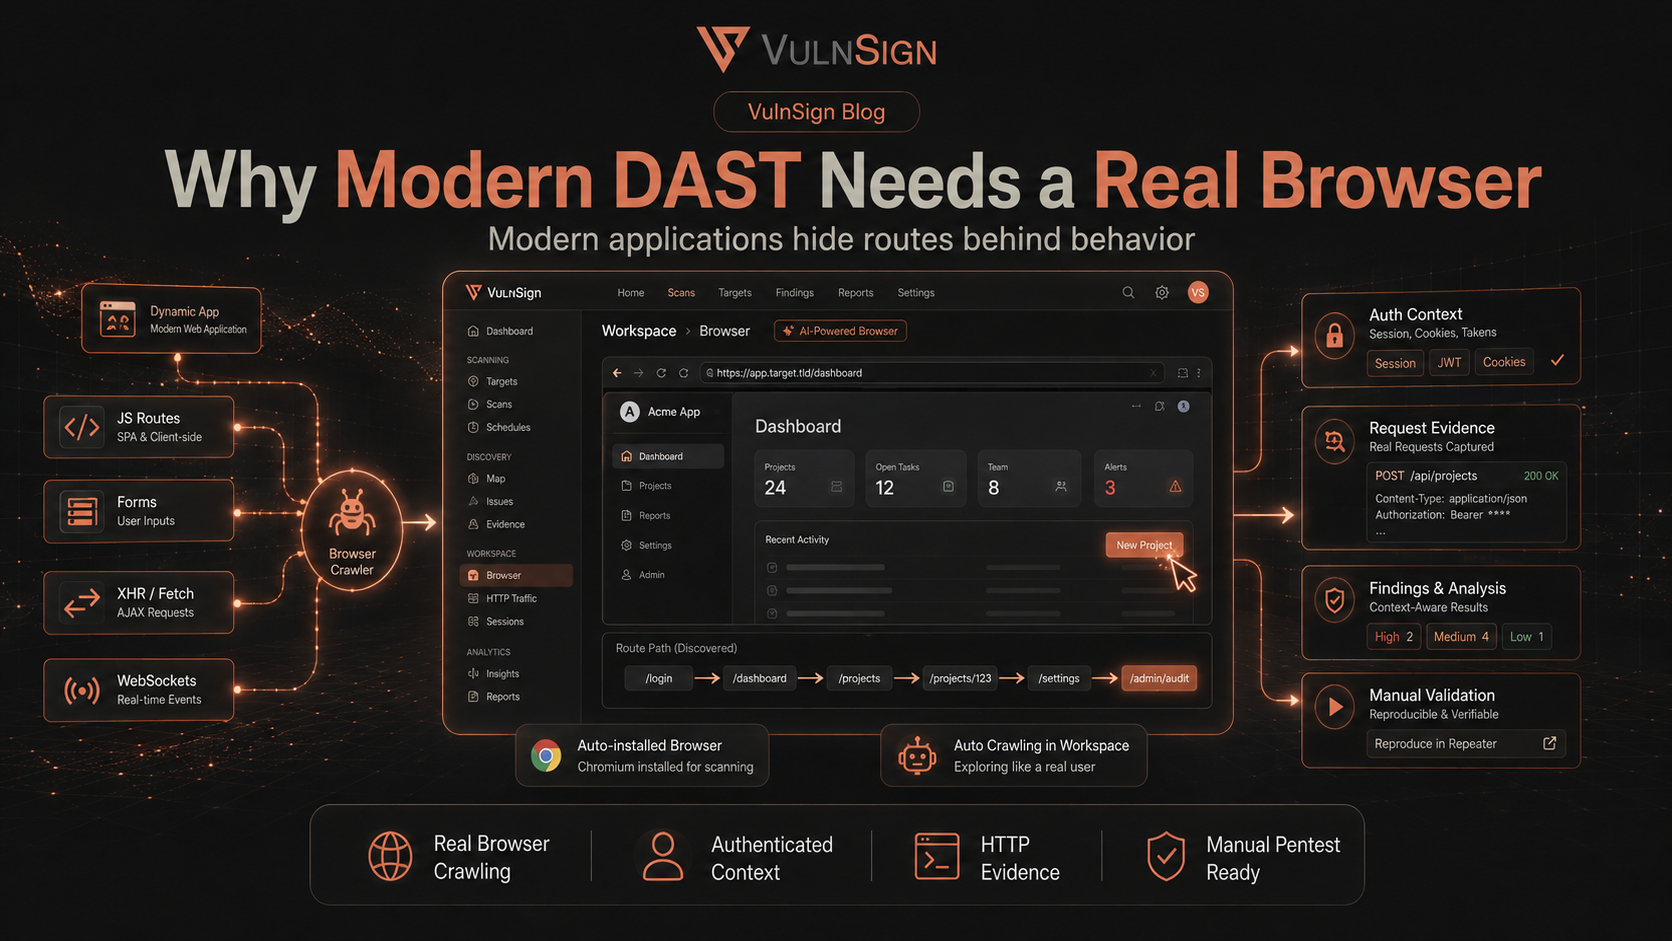
Why Modern DAST Needs a Real Browser
See how JavaScript execution, session state, and event-driven discovery reveal attack surface that link crawlers miss.
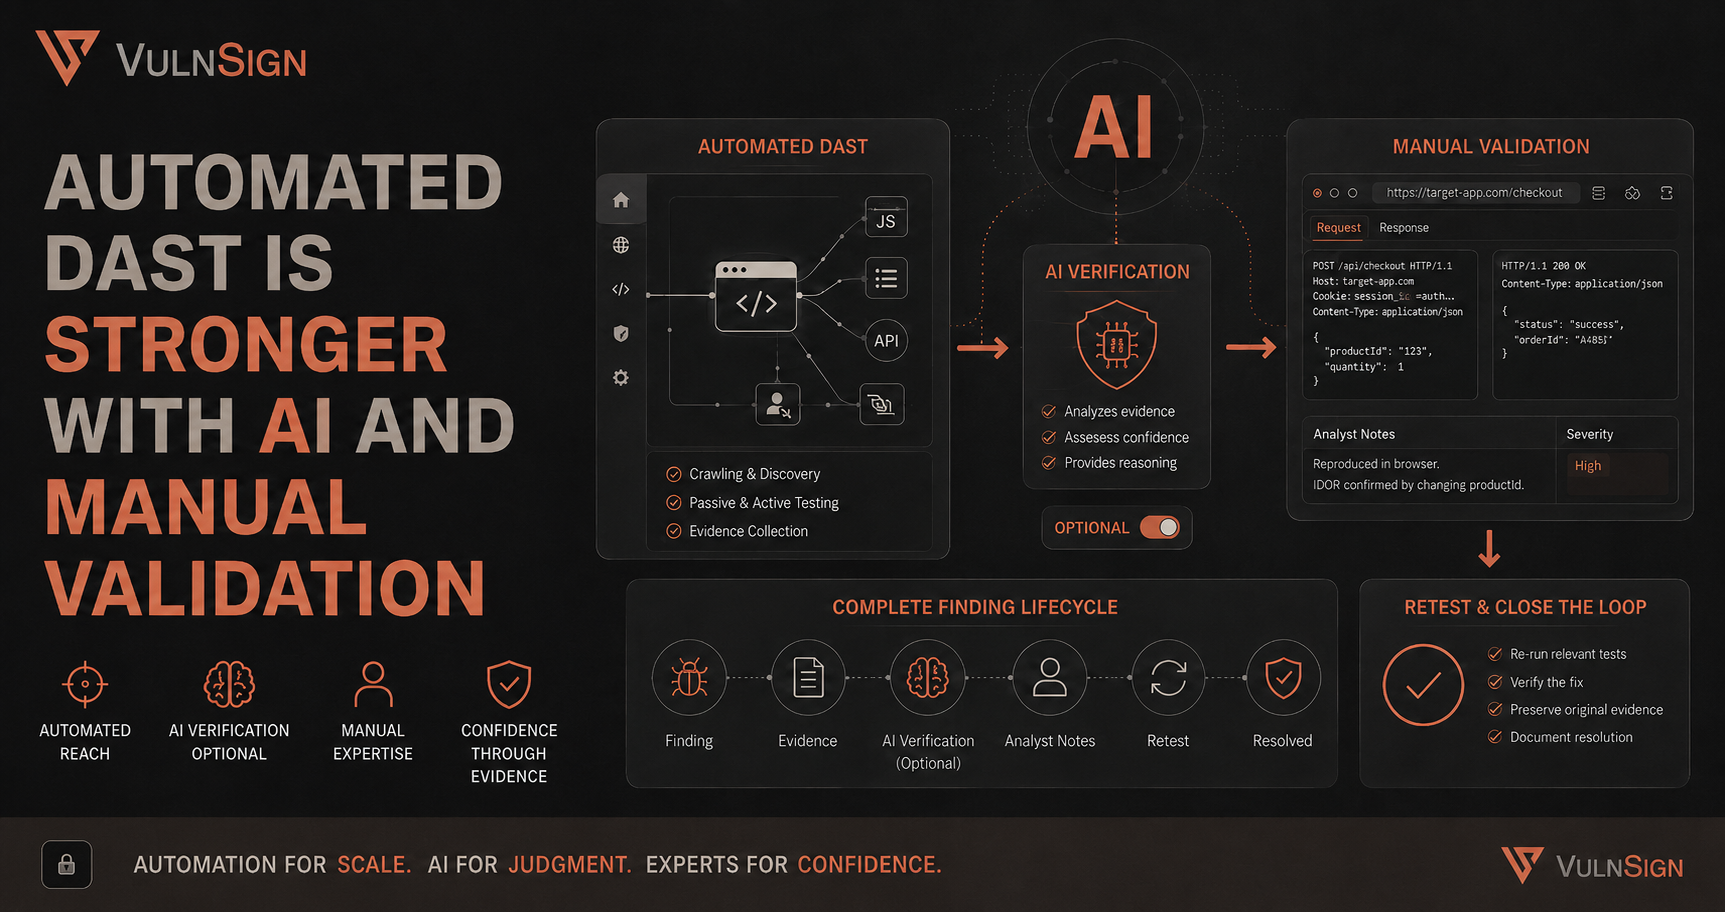
Automated DAST Is Stronger with AI and Manual Validation
Combine automated DAST with optional, model-selectable AI verification and hands-on analyst validation in one evidence-driven workflow.
Questions before you scan?
Learn how VulnSign fits into your environment, security workflow, and team.
Put automated and manual testing in one workflow.
See how VulnSign helps your team discover more attack surface, validate risk, and move findings to remediation—without sending security data to a cloud control plane.
Professional Android testing without leaving the DAST workflow
Install and verify the local Android toolchain with one click in the VulnSign desktop application, then launch the emulator from the Web UI to test apps, bypass modern mobile defenses, and analyze captured traffic.
One-click desktop setup
Install the complete Android toolchain before your first pentest
Open Android in the VulnSign desktop application and click Setup Android once. VulnSign automatically installs and verifies the emulator, ADB, Google Play system image, virtual device, Scrcpy, and Frida before handing the workflow over to the Web UI.
One click
Setup Android automates the complete installation.
Local toolchain
Install the SDK and runtime on your own machine.
Automatic checks
Verify every required component before launch.
Web UI handoff
Launch Android from a pentest workspace when ready.
One-click Android SDK setup
Run Setup Android in the VulnSign desktop application, verify every local component, then continue in the Web UI.
01
Setup Android
02
Verify tools
03
Launch in Web UI